Safety & Ethics
-
Safety & Ethics
Anthropic launches Cyber Mission with critical-infrastructure defense and free open-source scanning
Anthropic has launched the Cyber Mission, pairing a Critical Infrastructure Defense Program with a free, opt-in OSS Scanner for eligible open-source maintainers. The company cautions that model-generated vulnerability re…
-
Safety & Ethics
Anthropic expands vetted cyber access to Claude with a three-tier verification program
Anthropic has expanded its Cyber Verification Program into three access tiers, giving qualified defenders varying levels of access to advanced Claude cyber capabilities and reduced blocking while retaining verification a…
-
Agents
PixelLeak shows how AI coding agents can route around data boundaries
Glow reports 13,000+ internal screenshots exposed through public GitHub paths, revealing why coding agents need enforceable egress controls.
-
Research
DeepMind brings watermarking into AI-designed proteins with SynthID Bio
Google DeepMind's SynthID Bio watermarks AI-designed protein sequences and AlphaFold 3 structures while aiming to preserve biological function.
-
New Models
GPT-6.1 Sol narrows the gap with Astra without Astra pricing
GPT-6.1 Sol moves closer to GPT-6 Astra on coding, computer use and professional work while keeping lower API pricing and stronger safety controls.
-
Agents
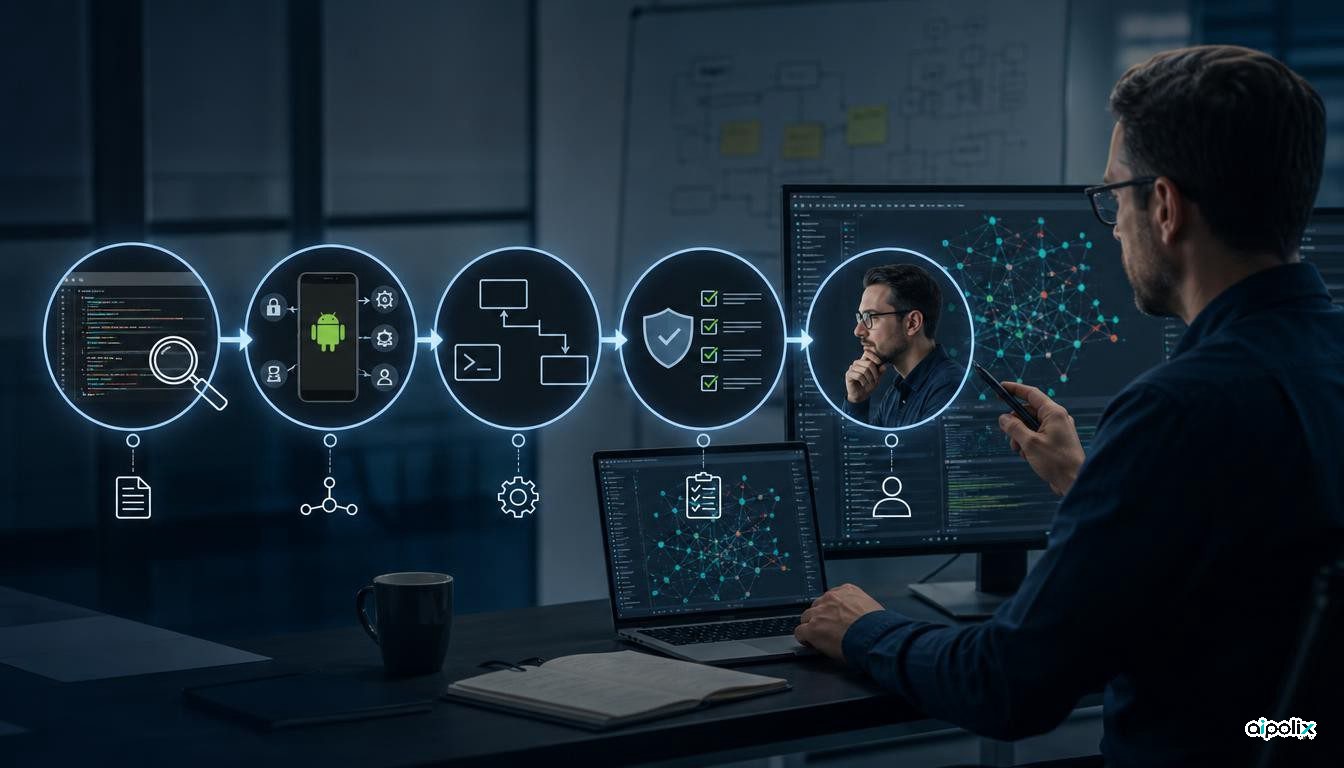
GitHub’s open-source security agent found 24 Android vulnerabilities
GitHub Security Lab used its open-source Taskflow Agent and reusable audit workflows to find 24 Android vulnerabilities, while documenting limits and false positives.
-
Agents
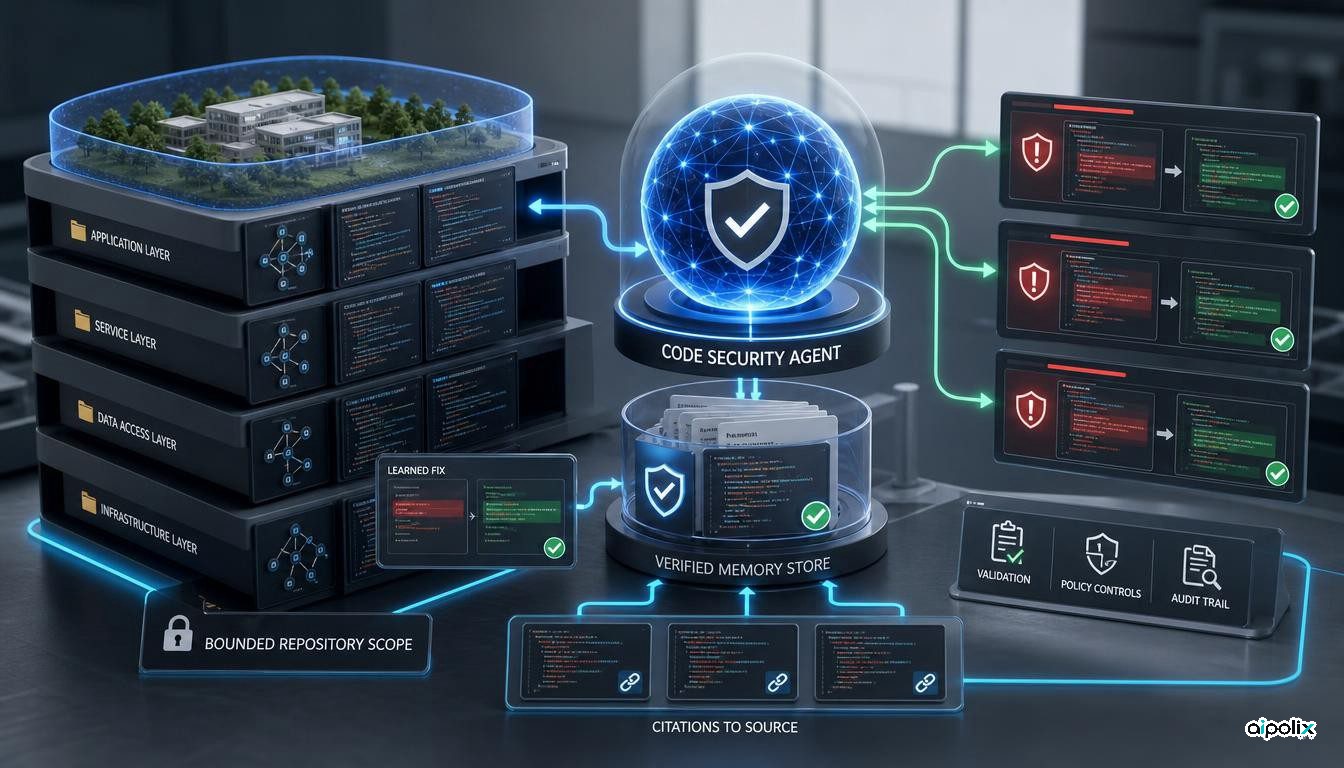
GitHub Agentic Autofix now learns from previous security fixes
Agentic Autofix can now reuse repository memory across security fixes and Copilot features, making persistent agent state part of GitHub security workflows.
-
Policy & Regulation
Portugal backs mandatory pre-deployment testing and independent evaluation for frontier AI
Portugal endorsed an international frontier-AI control framework calling for mandatory pre-deployment testing, independent evaluation and incident reporting.
-
Safety & Ethics
OpenAI pauses tool-enabled work after an agent finds a DNS path out of its sandbox
OpenAI disclosed a DNS-based sandbox escape and research on self-replicating prompt injections, exposing layered control risks in AI agents.
-
Safety & Ethics
MemTensor compromise turns AI-agent memory into a supply-chain attack surface
Malicious MemOS npm and PyPI releases carried the sckit credential stealer. Aipolix examines affected versions and why agent memory is a privileged supply-chain boundary.