
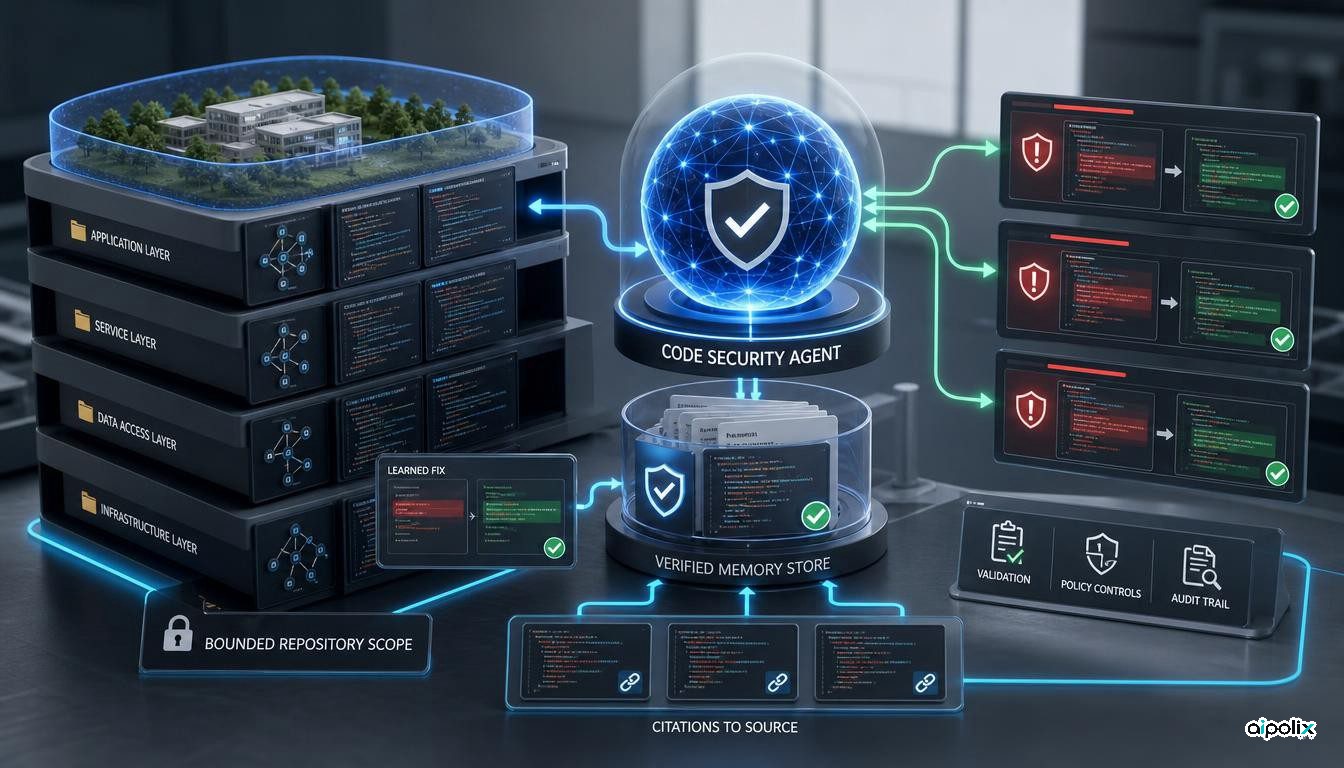
GitHub has connected Agentic Autofix to Copilot Memory, turning security remediation from a mostly per-alert activity into a process that can reuse repository-specific knowledge. For customers who have enabled Copilot Memory, Agentic Autofix now reads existing memories before working on a code-scanning alert and stores successful fix patterns back into memory after producing a fix.
GitHub says those stored patterns can later help resolve additional security alerts and can also inform other Copilot surfaces, including Copilot code review and Copilot cloud agent. Both Agentic Autofix and Copilot Memory remain in public preview.
The material change is persistence. Instead of treating each security alert as an isolated task, GitHub is allowing one remediation path to become context for later work in the same repository. That can reduce repeated reasoning about project conventions, but it also makes memory state part of the security-control boundary.
Security fixes can become reusable repository knowledge
Agentic Autofix already explores a repository, proposes a change and validates the result as part of an agent session. The new integration adds a learning loop around that process. Before attempting a fix, the agent can consult repository memories for conventions or patterns that may matter. After a successful fix, GitHub says the fix pattern can be stored for future use.
That is different from simply adding a longer prompt. A persistent memory can influence multiple later tasks and, according to GitHub, can be shared across supported Copilot features in the same repository. A remediation pattern learned while addressing one alert may therefore shape a future security fix or code review.
For teams, the practical benefit is continuity. A security agent does not need to rediscover every local convention on every alert. But continuity also creates a dependency: if stored knowledge is wrong, outdated or too broad, later automated work may inherit that problem.
GitHub validates repository memories before reuse
GitHub's Copilot Memory documentation describes an important safeguard. Repository-level facts are stored with citations to supporting code. When a fact becomes relevant again, Copilot checks those citations against the current branch and only uses the fact if it still validates.
Unused facts and preferences are automatically deleted after 28 days, although the timer can reset when an entry is successfully validated and used. Repository owners can also review and manually delete stored repository facts.
Those controls reduce the risk of stale memory becoming permanent policy, but they do not eliminate governance questions. The memory is still generated from Copilot activity, and the feature is in public preview. Teams need to understand which stored facts exist, who can create them, how they are scoped, and when a human should remove or override them.
The Aipolix conclusion is that memory for security automation should be treated like other durable configuration: it deserves visibility, lifecycle controls and a clear ownership model.
Cross-feature memory expands the blast radius of a mistake
GitHub's documentation says repository-level memories can be used by several Copilot features, including Copilot cloud agent, Copilot code review, Copilot CLI and Agentic Autofix. This makes the memory layer more valuable, but also more consequential.
A correct repository convention can help multiple tools behave consistently. An incorrect or misleading memory can potentially influence more than one workflow. The problem is not that shared memory is inherently unsafe; it is that shared state changes the scope of a mistake.
For security remediation, this is especially important. A remembered fix pattern may encode a repository-specific way to handle authentication, validation or dependency updates. Reusing that pattern can save time, but it should not be confused with proof that the same fix is correct for every future alert.
GitHub itself does not claim that the integration guarantees better security outcomes. The September 25 announcement contains no benchmark for fix accuracy, false-positive rates or vulnerability recurrence.
Public preview status still matters
Both Agentic Autofix and Copilot Memory are public previews, so organizations should expect behavior and controls to evolve. GitHub's documentation also makes clear that memory must be enabled before the integration applies.
Agentic Autofix is part of GitHub's code-scanning remediation flow and uses an agent session to explore the codebase, generate a fix, validate it and open a change for review. The memory integration does not remove the need for review, policy controls or independent security testing.
A system that remembers previous fixes may appear more experienced, but accumulated context is not the same as verified correctness. Persistent context can improve consistency while still carrying forward an earlier misunderstanding.
Memory becomes part of the security architecture
The broader implication is that agent memory is moving from convenience feature to infrastructure. Once an automated security tool can learn from one alert and reuse that learning across later alerts and Copilot features, memory becomes part of how the system makes decisions.
That means teams should ask operational questions alongside model-quality questions: What is stored? What evidence supports it? How long does it live? Which features can consume it? Who can delete it? What happens when repository architecture changes?
GitHub has already implemented some of those answers through citation validation, repository scoping, manual deletion and automatic expiry for unused memories. The remaining question is organizational: whether teams treat that state as something worth monitoring.
Agentic Autofix using Copilot Memory is therefore more than a convenience update. It is a small but meaningful example of security automation becoming stateful. The benefit is that the agent can carry repository-specific lessons forward. The trade-off is that memory quality and governance now influence more than one security task.