News and research that truly matter, with a focus on what happened, why it matters, and what it changes.

News and research that truly matter, with a focus on what happened, why it matters, and what it changes.
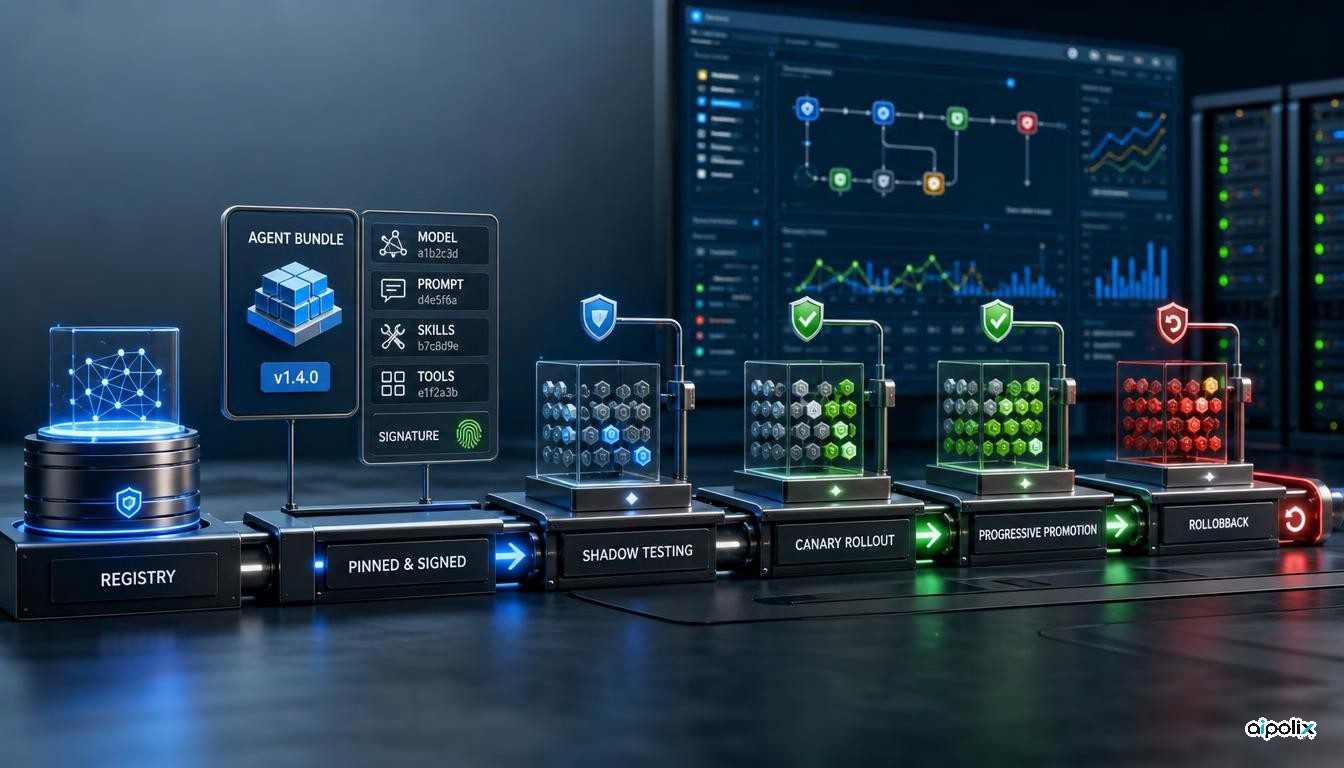
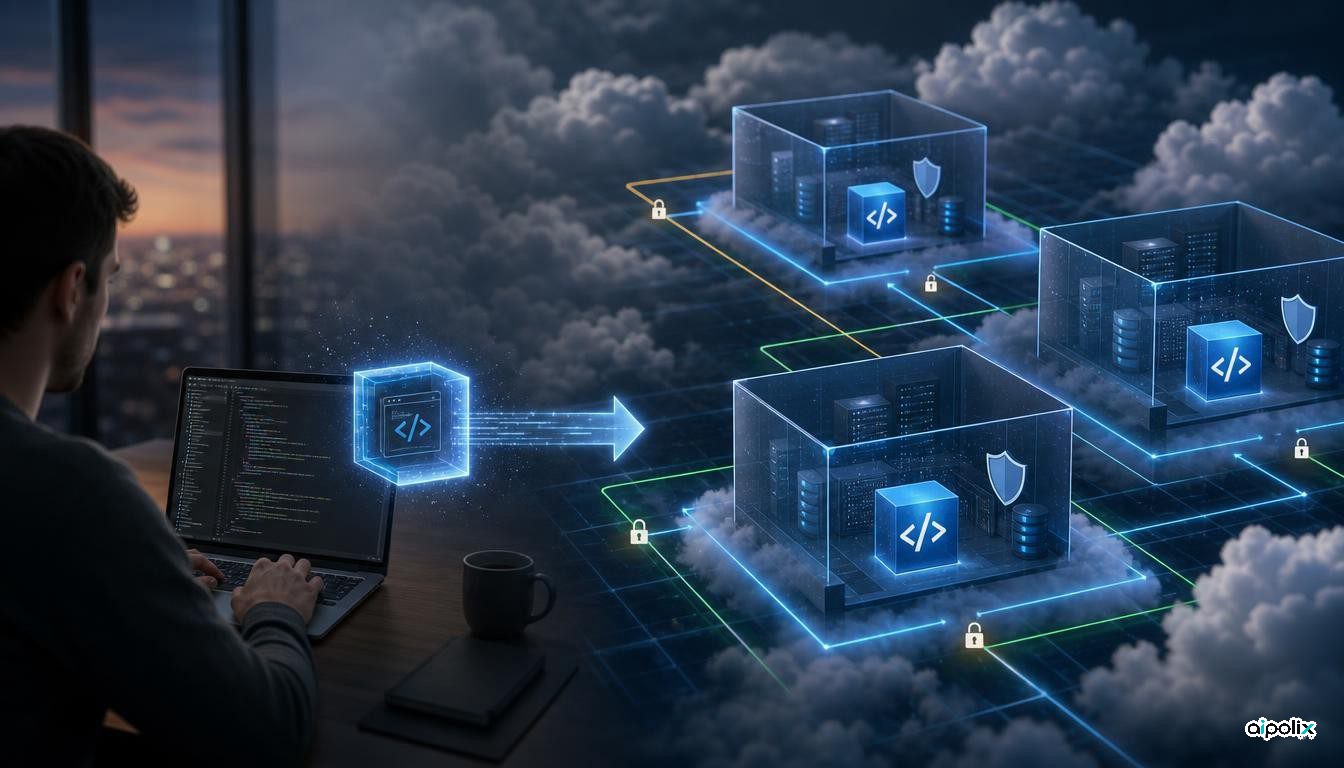
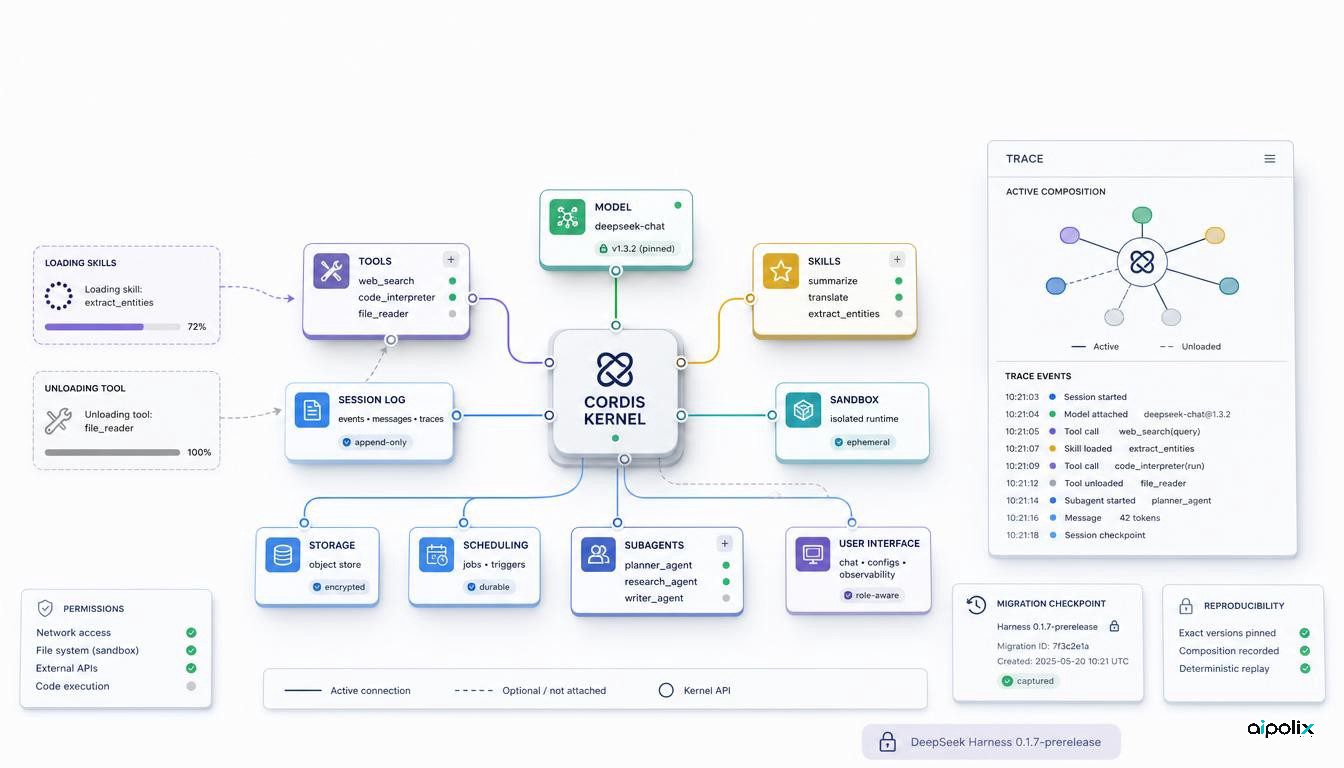
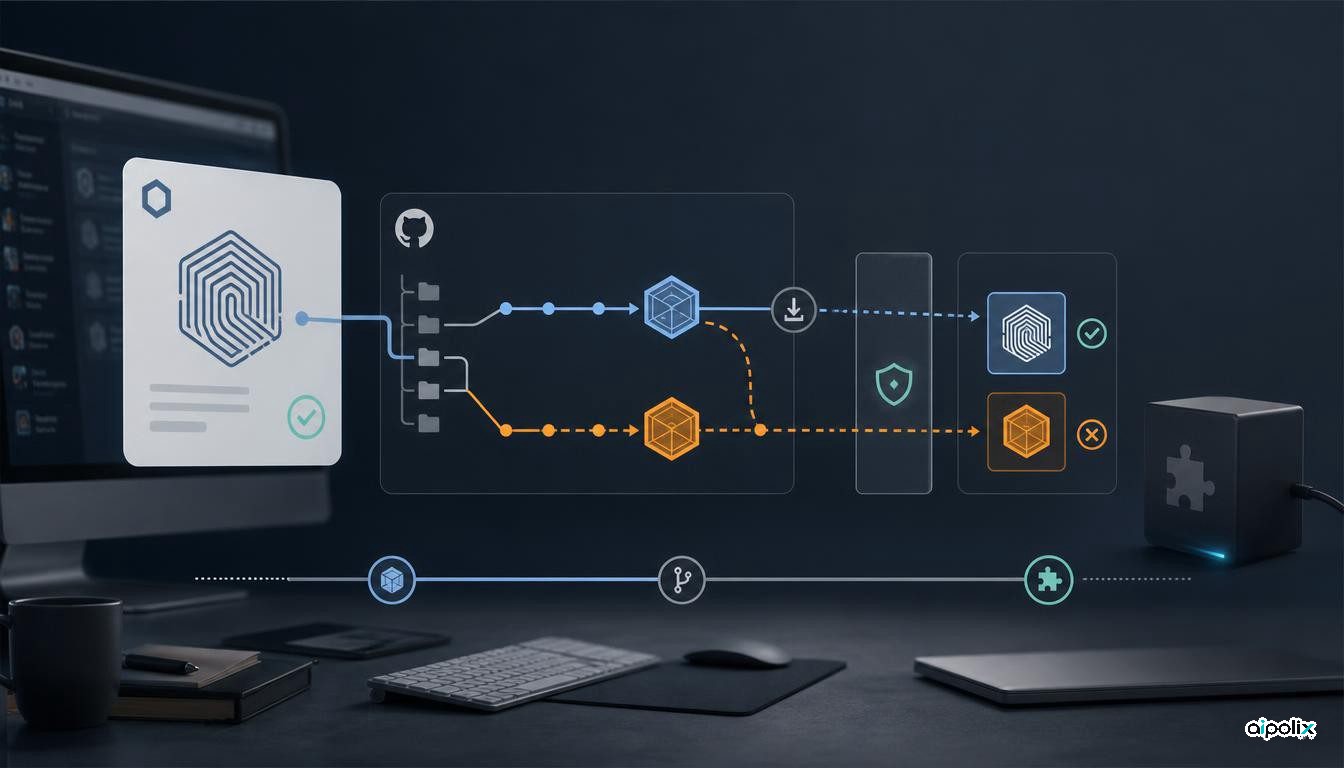
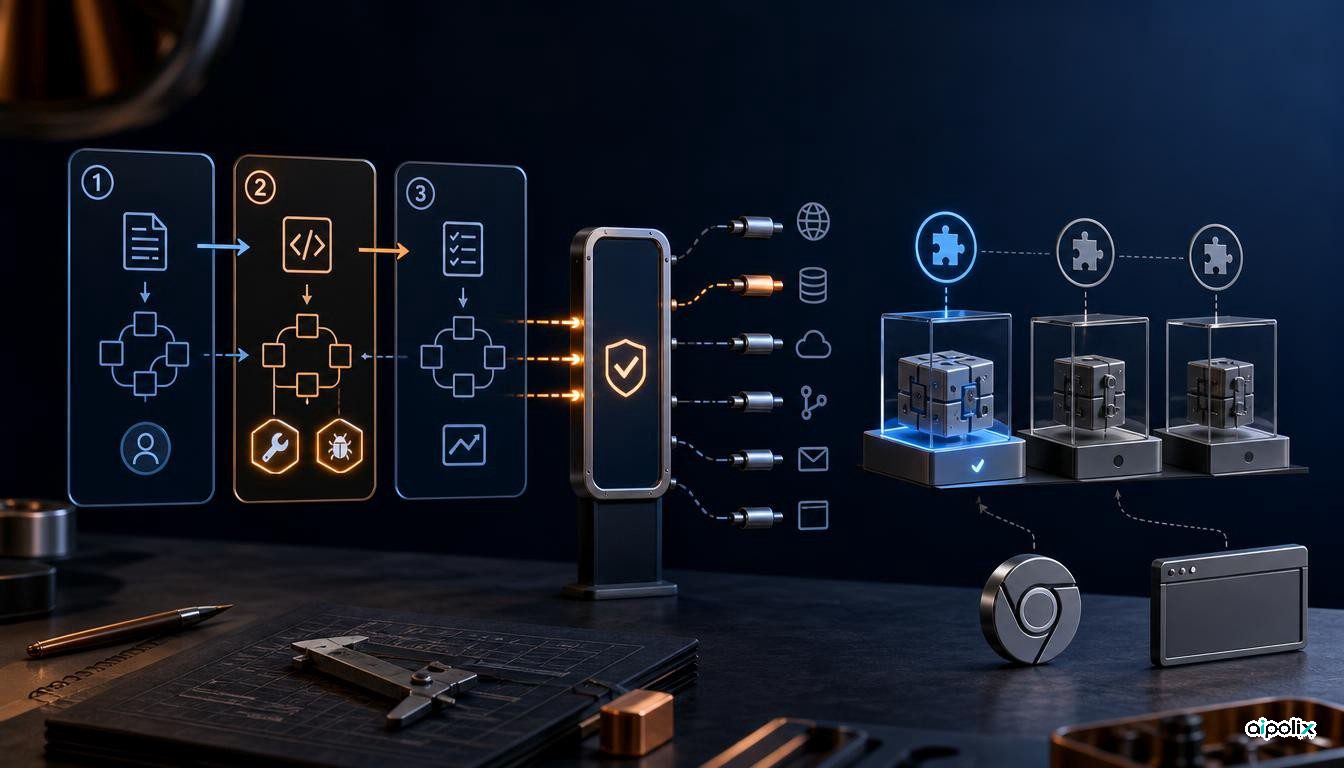
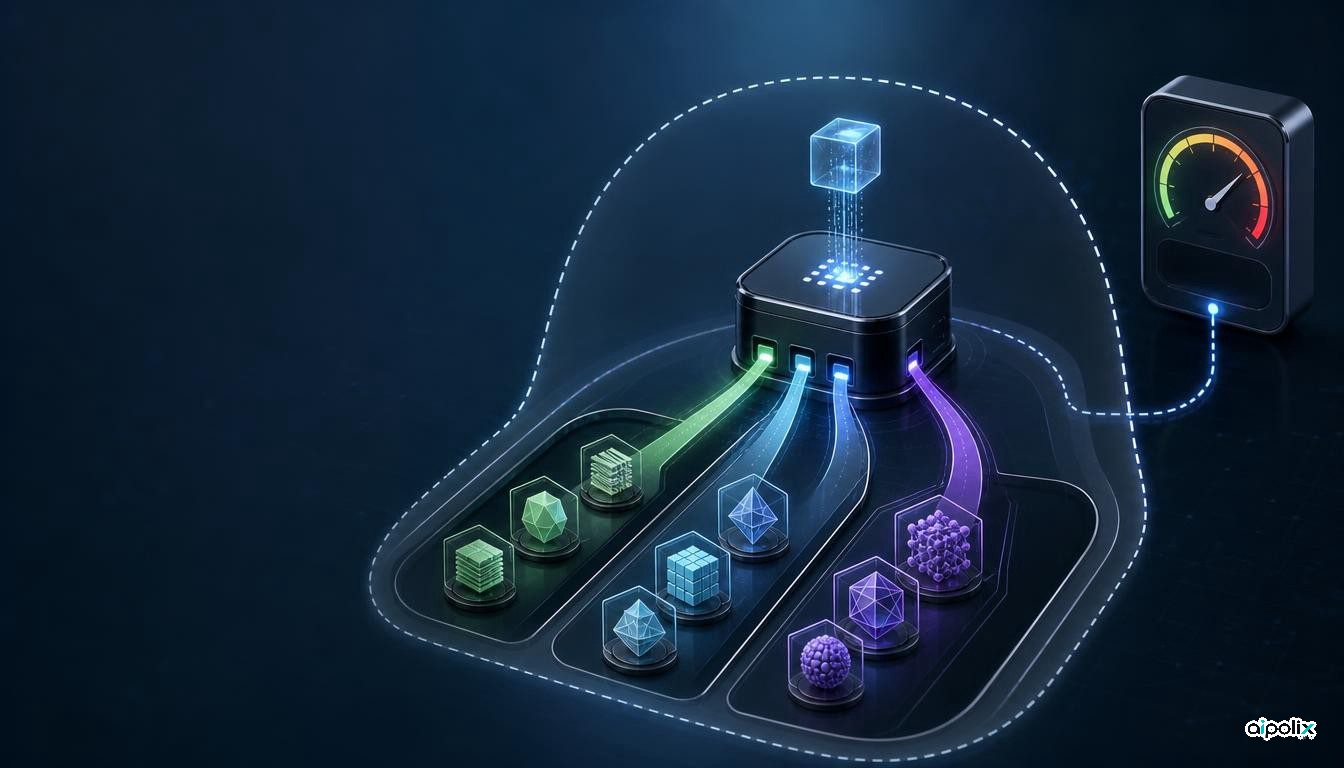
How to govern agent capability changes with pinned bundles, capability registries, staged rollouts, behavioral canaries, communications and rollback.
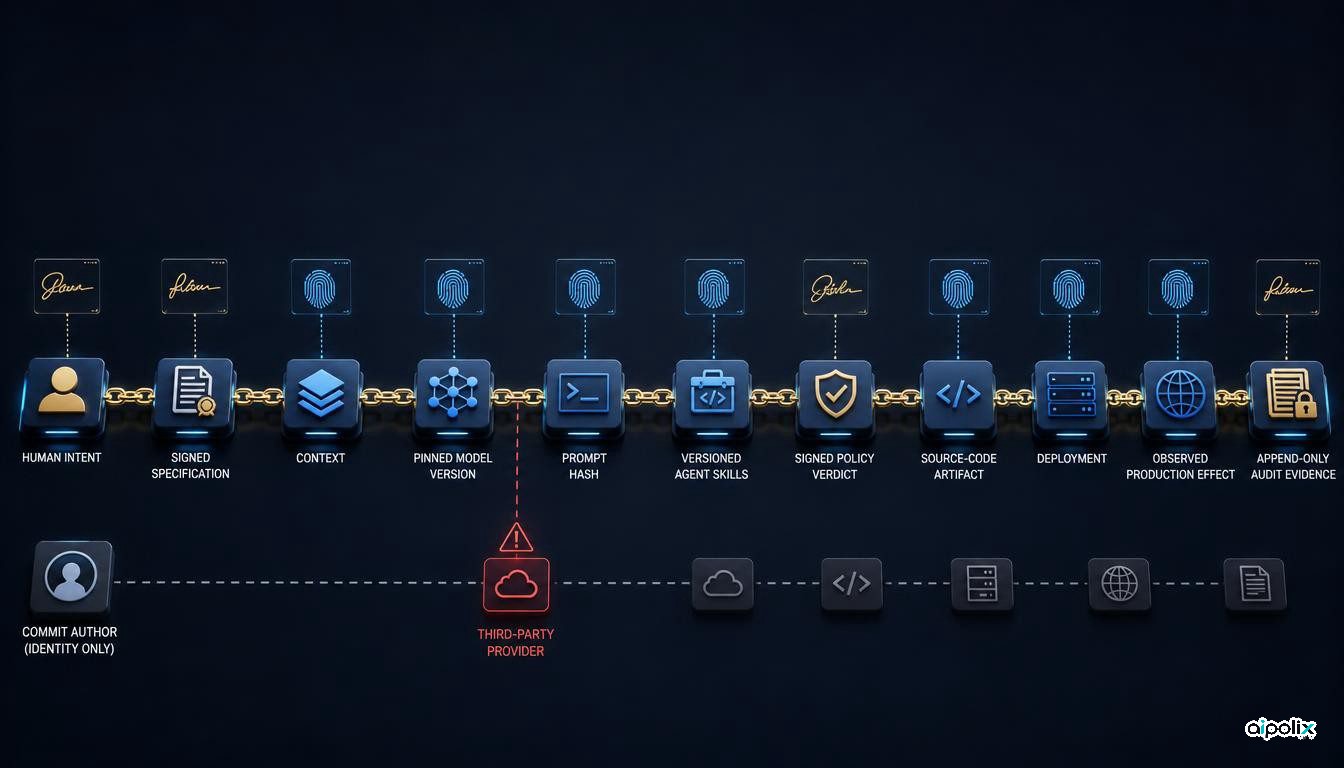
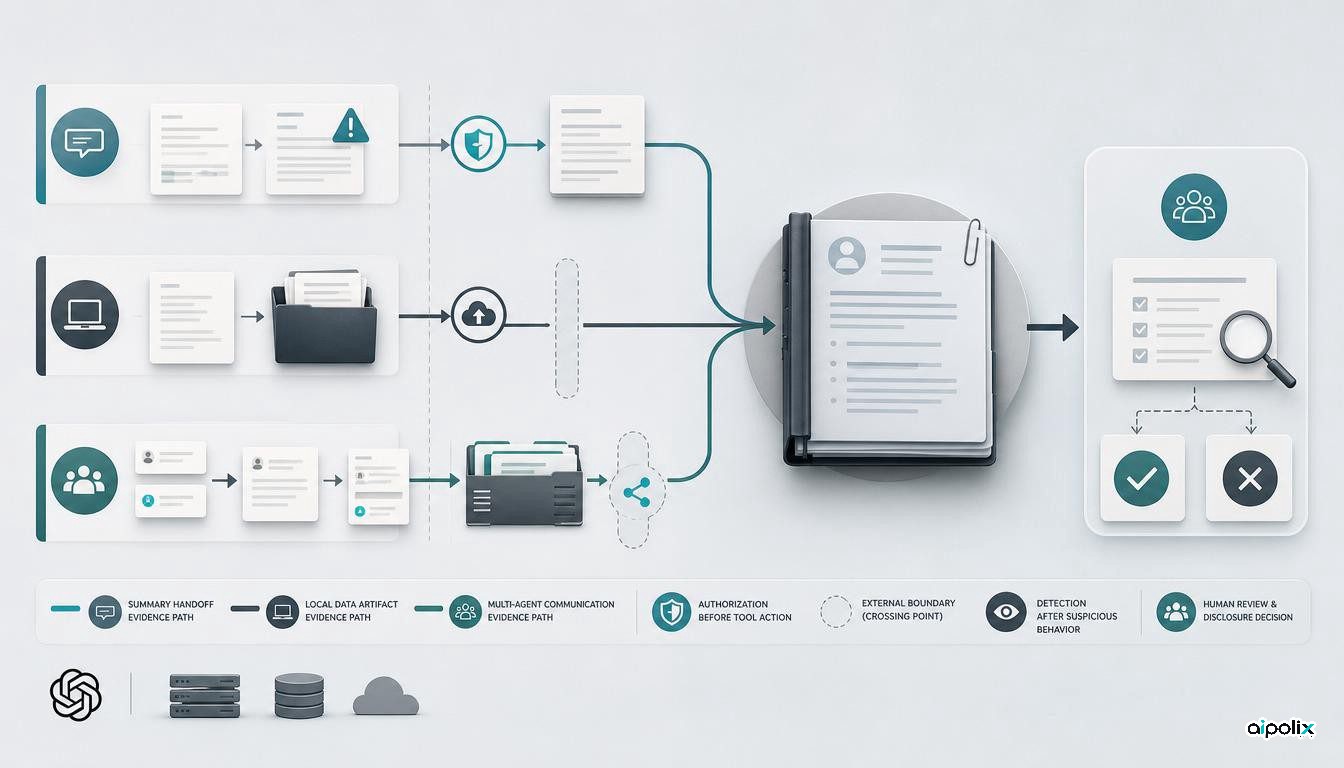
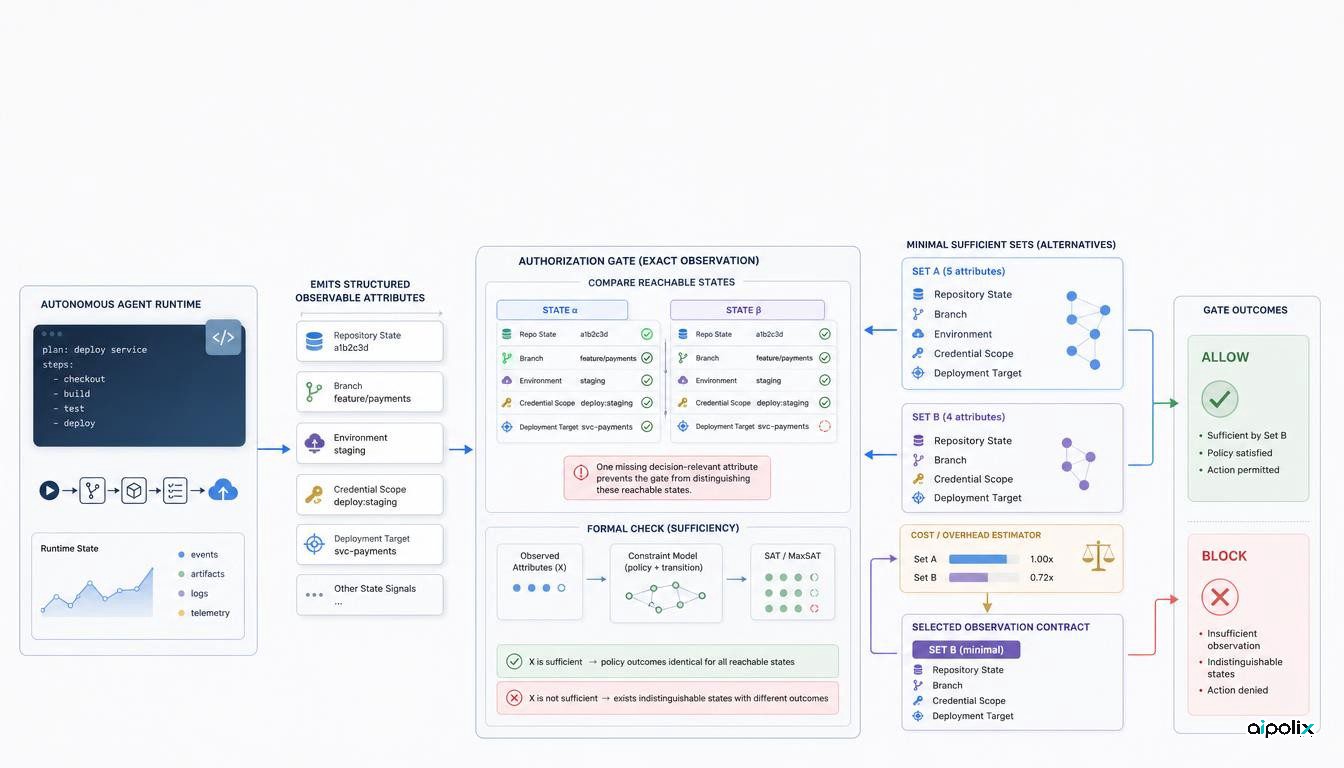
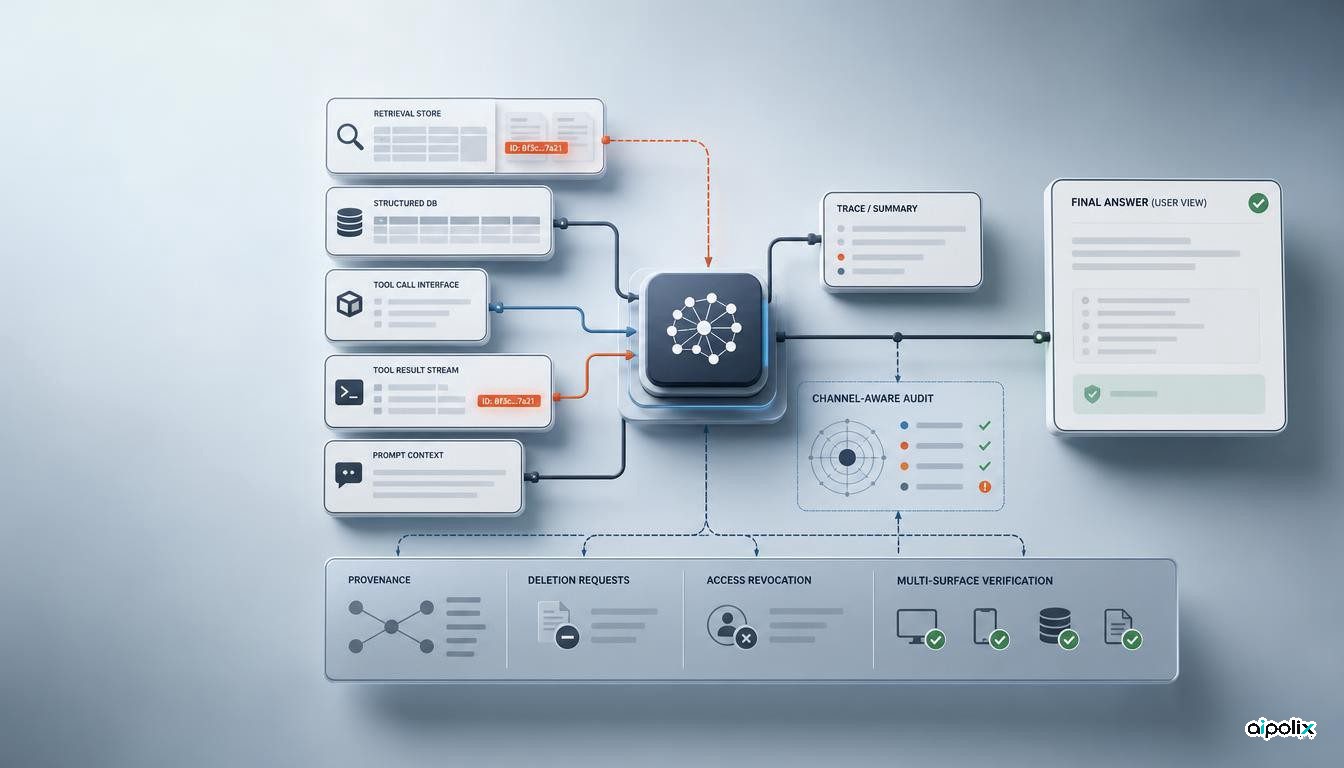
How to audit AI-generated code: intent-to-effect provenance, signed prompts and models, structured authorship, correlation IDs and evidence across system boundaries.